Logo home 9

Over 10 years we helping companies reach their financial and branding goals. Onum is a values-driven SEO agency dedicated.

CONTACTS
Embedded IoT Solutions

IoT Security for Connected Products: Beyond the Technical Controls

Category
Embedded IoT Solutions
Read Time
6 min read
Published
May 21, 2026
Status
Published

The controls are the part teams eventually get right. What decides whether a company has a bad year is who owns security, and whether anyone is still patching in year four.

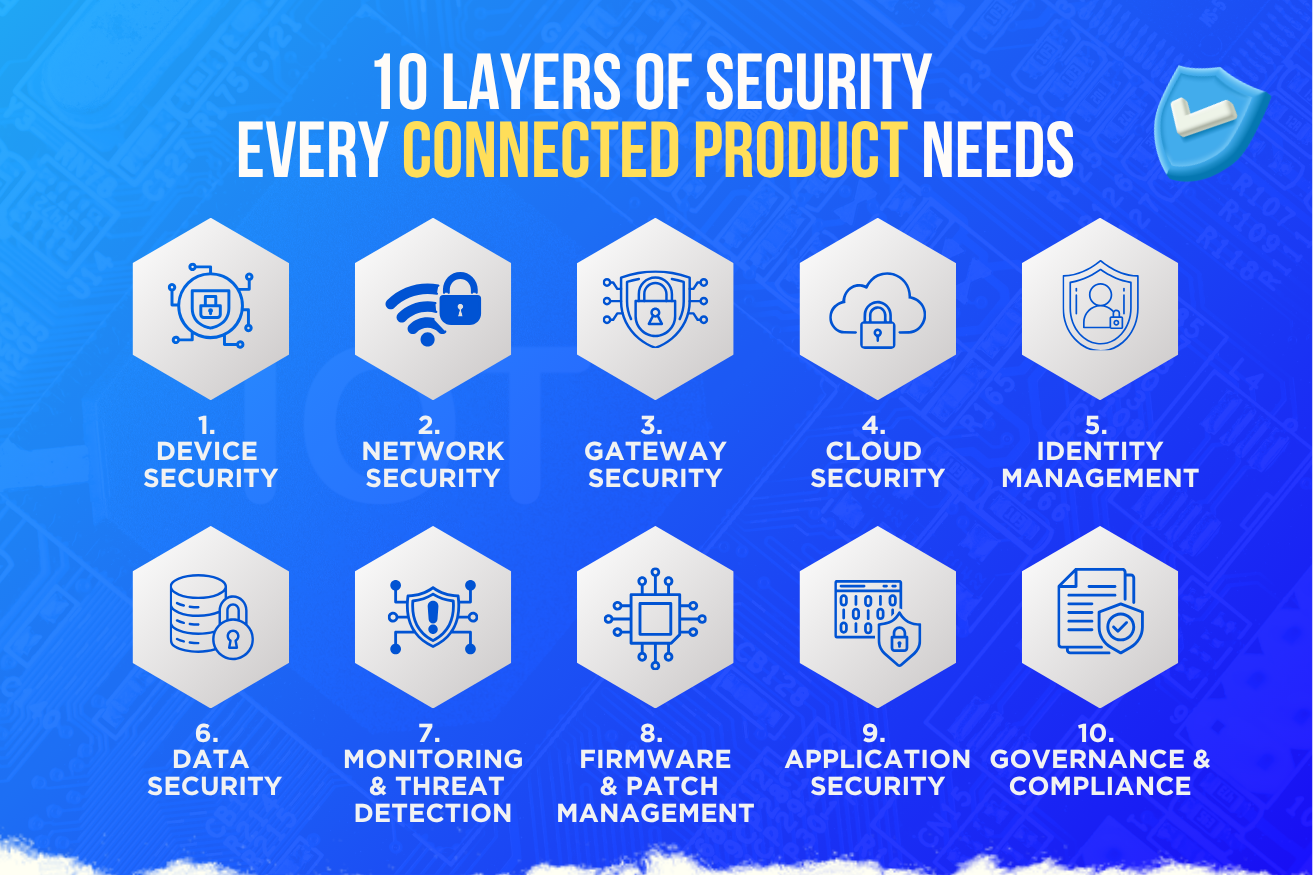
Technical controls — secure boot, encrypted transport, per-device certificates — are the part of IoT security teams usually get right eventually. The part that decides whether a company has a bad year is organisational: who is responsible, what was promised to customers, how a report from a researcher is handled, and whether anyone is still patching the product in year four.

This guide covers that side of connected product security: threat modelling that fits the business, the obligations that now come with selling a connected device, and the processes that turn security from a launch task into something sustained. For the device-level controls themselves, see IoT device security.

Framing

Why Connected Products Change the Risk

A security failure in a web application exposes data. A security failure in a connected product can also open a door, stop a pump, or give an attacker a foothold inside a customer’s network. Three characteristics make the risk different in kind.

  • Physical consequence. Devices act on the world, so compromise can cause damage rather than only disclosure.
  • Physical access. An attacker can buy your product, open it, and probe it at leisure. Any secret present on one device must be assumed extractable.
  • Long life, slow patching. A device shipped today may run for a decade, often unattended, sometimes with no one left responsible for it.

Assume one device will be taken apart by a determined attacker. Design so that this does not compromise the other ten thousand.

That single assumption rules out the most common serious mistake: a shared key or password across a product line, where extracting it from one unit yields control of the fleet.

Method

Threat Modelling That Is Worth the Afternoon

Formal methodologies are useful, but most teams get the majority of the benefit from four structured questions, answered honestly in one session with hardware, firmware, cloud and product people present.

1

What would an attacker want here?

Data, control of the device, a route into the customer’s network, or free use of a paid service. The answer shapes everything; a product whose value to an attacker is network access needs different defences from one holding personal data.

2

Where are the boundaries?

List every point where data or commands cross trust lines: device to cloud, app to cloud, device to local network, physical ports, the update channel, and the manufacturing line. Boundaries are where controls belong.

3

What happens if one device is fully compromised?

Can it read others’ data? Issue commands beyond itself? Impersonate the fleet? If yes to any, the architecture needs per-device identity and authorisation rather than a stronger device.

4

What is the worst realistic outcome?

A privacy breach, a safety incident, a fleet-wide outage, or a botnet built from your product. Rank by consequence rather than likelihood, because low-probability high-consequence outcomes are what end businesses.

Obligations

What Selling a Connected Product Now Commits You To

Unique credentials per device
Default or shared passwords are now explicitly prohibited in several markets, and are the single most cited cause of large IoT botnets.
A stated support period
Buyers and regulators increasingly expect a published date until which security updates will be provided. Vague answers are becoming a procurement obstacle.
A vulnerability disclosure route
A documented way for researchers to report problems, with a commitment to respond. Without one, the first notification may be a public post.
Knowing what is inside your firmware
A component inventory is what lets you answer “are we affected?” within hours of a library vulnerability. Reconstructing it under pressure is far harder.
Data handling that matches what you promised
Retention, residency, access, and deletion. Security and privacy obligations overlap, and customers increasingly ask about both in writing before purchase.
Process

Keeping Security Alive After Launch

1Name an owner
One person accountable for the product’s security posture after the launch team moves on. Without a name, patching stops quietly and nobody notices for a year.
2Maintain a component inventory
Every library and version in the firmware and backend, generated by the build rather than maintained by hand, so vulnerability questions take minutes.
3Rehearse an emergency update
Practise shipping a critical patch end to end, including rollback. The first time should not be during an actual incident.
4Protect the signing keys properly
Whoever holds them controls every device you have shipped. Hardware-backed storage, limited access, and a documented rotation plan are proportionate.
5Monitor the fleet for anomalies
Unusual traffic, authentication failures, or devices appearing in unexpected regions are often the first sign of compromise — and are invisible without baseline fleet metrics.
6Test like an attacker before shipping
Open the device, probe debug interfaces, dump the flash, intercept traffic. An external assessment finds things the team that built it cannot see.
FAQ

Frequently Asked Questions

Why is security different for connected products?
Because devices act physically, so compromise can cause damage rather than only data loss; because attackers can buy a unit and probe it indefinitely, meaning any on-device secret is extractable; and because products run for years, often unattended and long after anyone is actively maintaining them.
What is the most common serious IoT security mistake?
Shared credentials across a product line. Extracting a key or password from one physically accessible device then yields control of every unit, which is how large IoT botnets have repeatedly been assembled. Per-device identity is the structural fix.
How do you threat model an IoT product quickly?
In one session with hardware, firmware, cloud and product people, answer four questions: what an attacker would want, where data and commands cross trust boundaries, what one fully compromised device could do to the rest, and what the worst realistic outcome would be.
What are buyers and regulators now expecting?
Unique per-device credentials rather than defaults, a published date until which security updates will be provided, a documented vulnerability disclosure route, knowledge of which software components are inside the firmware, and data handling that matches what was promised.
How do you keep an IoT product secure years after launch?
Name an accountable owner, maintain a build-generated component inventory so vulnerability questions take minutes, rehearse emergency updates including rollback, protect signing keys in hardware-backed storage, and monitor fleet behaviour for anomalies against a known baseline.
Wrapping Up

Conclusion

Securing a connected product is less about any individual control than about sustaining responsibility. The technical measures are well documented and increasingly standard; what separates companies is whether someone owns the posture, knows what is inside the firmware, can ship an emergency patch today, and has told customers how long support lasts.

Assume one device will be fully compromised and design so the fleet survives it. Then treat security as an operating commitment with a name attached, not a milestone that was passed before launch.

The same principles now apply to AI agents that hold credentials and act on business systems. AI agent security shows how least privilege and audit trails carry over.

About MetaDesk Global

Engineering the Next Generation of Connected Products

MetaDesk Global helps startups and enterprises develop intelligent connected products that combine embedded systems, Industrial IoT, Edge AI, and cloud technologies. Our expertise includes:

Industrial IoT (IIoT) Solutions Embedded Firmware Development Edge AI Development Predictive Maintenance Systems PCB Design IoT Gateway Development Cloud Integration OTA Firmware Updates AIoT Product Development End-to-End Product Engineering

From hardware design to AI-powered industrial platforms, we build scalable solutions for the next generation of connected products.

Start Your Project

Building a Connected Product?

We design IIoT sensor networks, Edge AI pipelines, and secure cloud platforms — from prototype to production.

Request a Free Quote →